Introduction
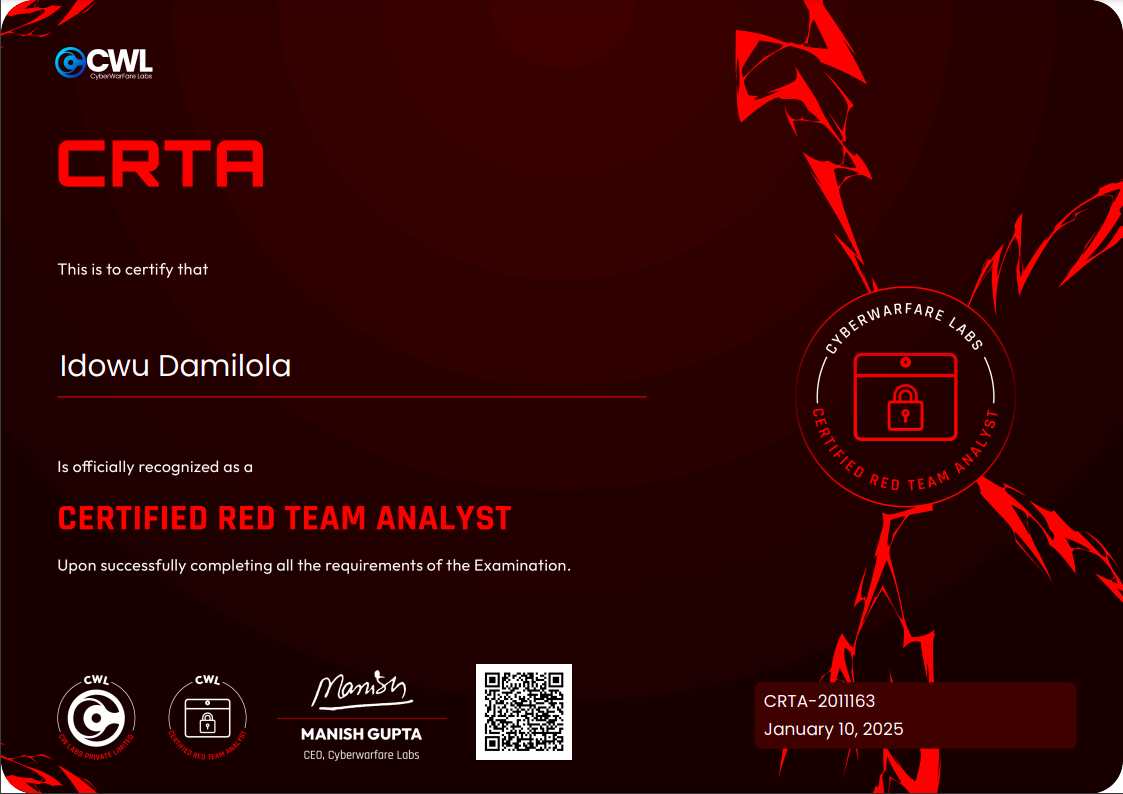
The Certified Red Team Analyst [CRTA] certification is a fully hands-on course for Beginners who want to level up their understanding about red teaming. Upon registering for this course you are given access to the course, labs and 2 exam retake (cool).
I wrote the CRTA exam from Cyberwarfare labs 8th January 2025 and the experience was superb.
I have really gone back and forth on whether or not to give it a review and after thinking about the experience I think CWL did a good one on this certification. Also writing this to encourage every beginner/advanced red teamer out there to give it a try, really no knowledge is wasted.
https://portal.cyberwarfare.live/login
My take on the course
This course provides an in-depth introduction to Red Teaming, focusing on simulating realistic cyber attacks to identify vulnerabilities in an organization's infrastructure. Key topics include understanding the Red Team attack lifecycle, setting up Red Team labs (both external and internal), exploiting web, network, and cloud technologies, and performing post-exploitation tasks. Students will gain hands-on experience with real-world tools and tactics, including Active Directory exploitation, network pivoting, and stealth persistence. The course also integrates the MITRE ATT&CK framework and prepares students for a practical case study and examination.
You have the option of the video and pdf, which ever way of learning you prefer.
My Take on the labs
After registering for the certification you are given a 30 days lab access which you can activate anytime.
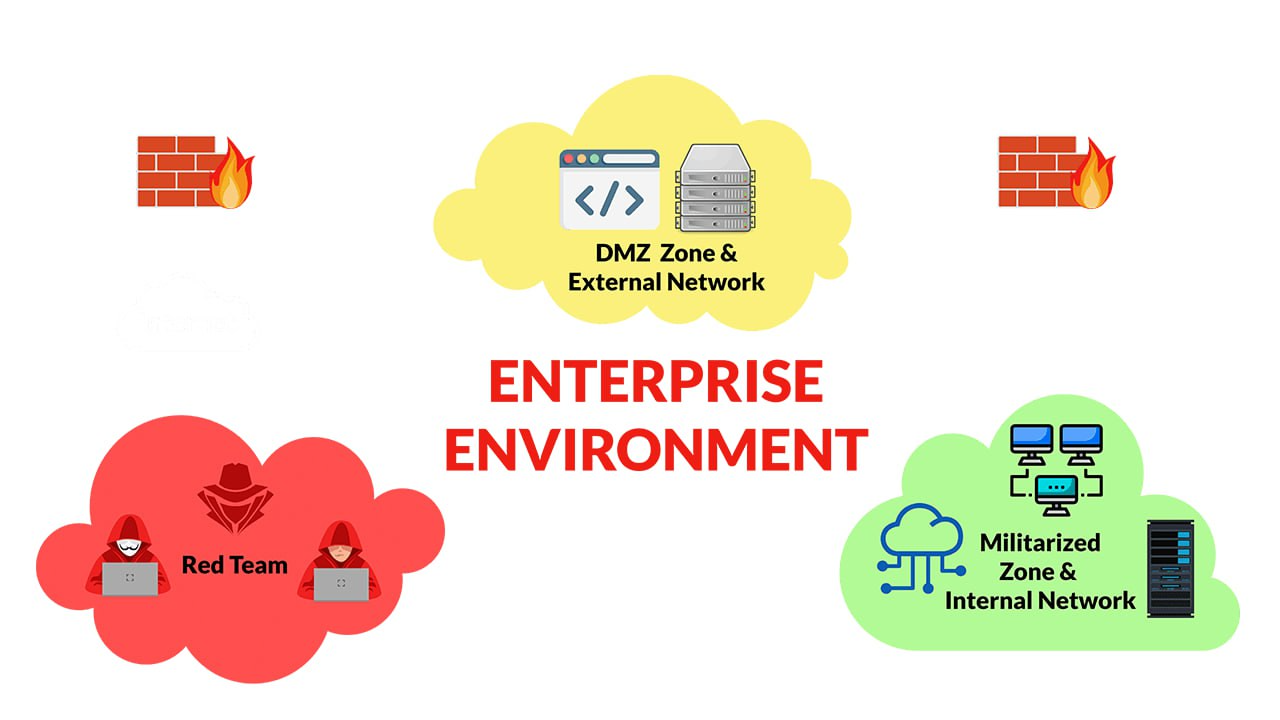
This lab aims to provide candidates with a robust external & internal (AD) red teaming. You are tasked to follow the videos for scope of engagements & complete the operations.
My Take on the exam
After finishing the course and labs I assure you, you are ready to take the exam. Everything you learn from the course and labs is fully applied in the exam.
For the exam process all you have to do is this:
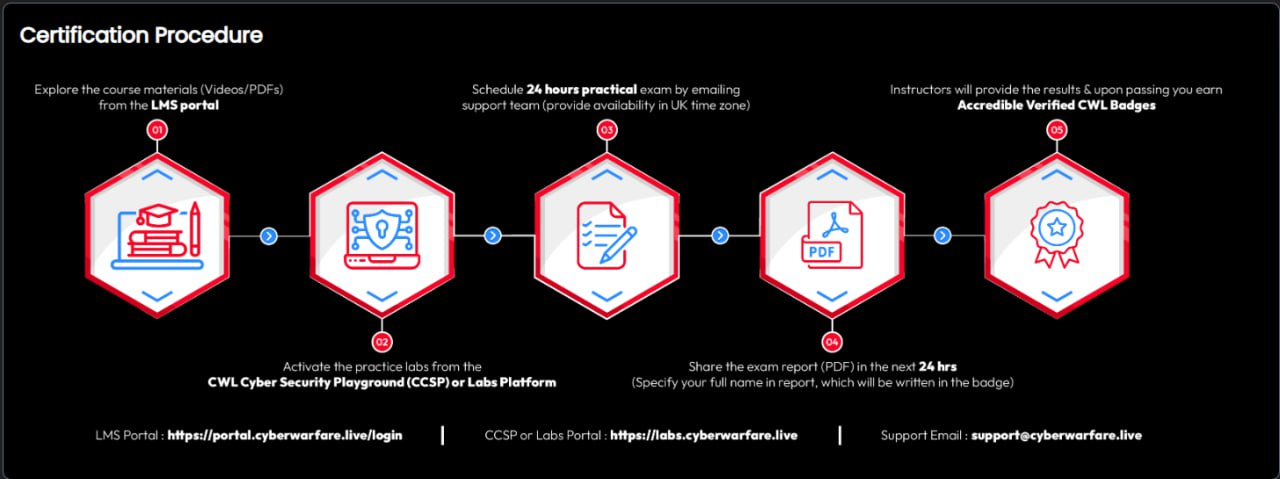
The exam was very calm in my opinion and was challenging as well but after practicing and going through what was learn't in the course/labs I was able to successfully capture the goal of the exam.
My Strategy
While I took the course and watch all videos, the course was smooth and anything I didn't understand I had to do my research on that topic for further learning, one thing I need to point out is that the course material and content is actually enough for your learning.
For the labs you have 30 days of lab access, I had to practice every thing I learnt in the course but when ever i got stuck I did extra research and sort to the lab walk through provided by CWL to help understand what was done in that scenario.
HINT HINT HINT
As said earlier the exam is actually challenging but all you need is already detailed in the course and the labs but for those very curious the exam is an AD based environment and things you would potentially need and do are;
- Have a good understanding on enumeration.
- Have a good understanding of network pivoting.
- Have a good understanding on proxy-chains.
- Have a good understanding on how to search for exploits.
- Have a good understanding on password spraying and pass the hash attacks.
- Have a good understanding on AD attacks and how to carry them out.
- Have a good understanding on data ex-filtration.
- Have a good understanding on report writing.
Finally
I submitted my report ensuring all screenshots were properly taken and made sure all my steps were clear like I would do if i was presenting a pertest engagement to a client.
Submitted the report and then BOOM, I passed.
Wishing all potential students of the CRTA a good one. Lets have fun.